Closing crypto’s screening gap: zeroShadow’s Casey Golden on real-time threat intelligence
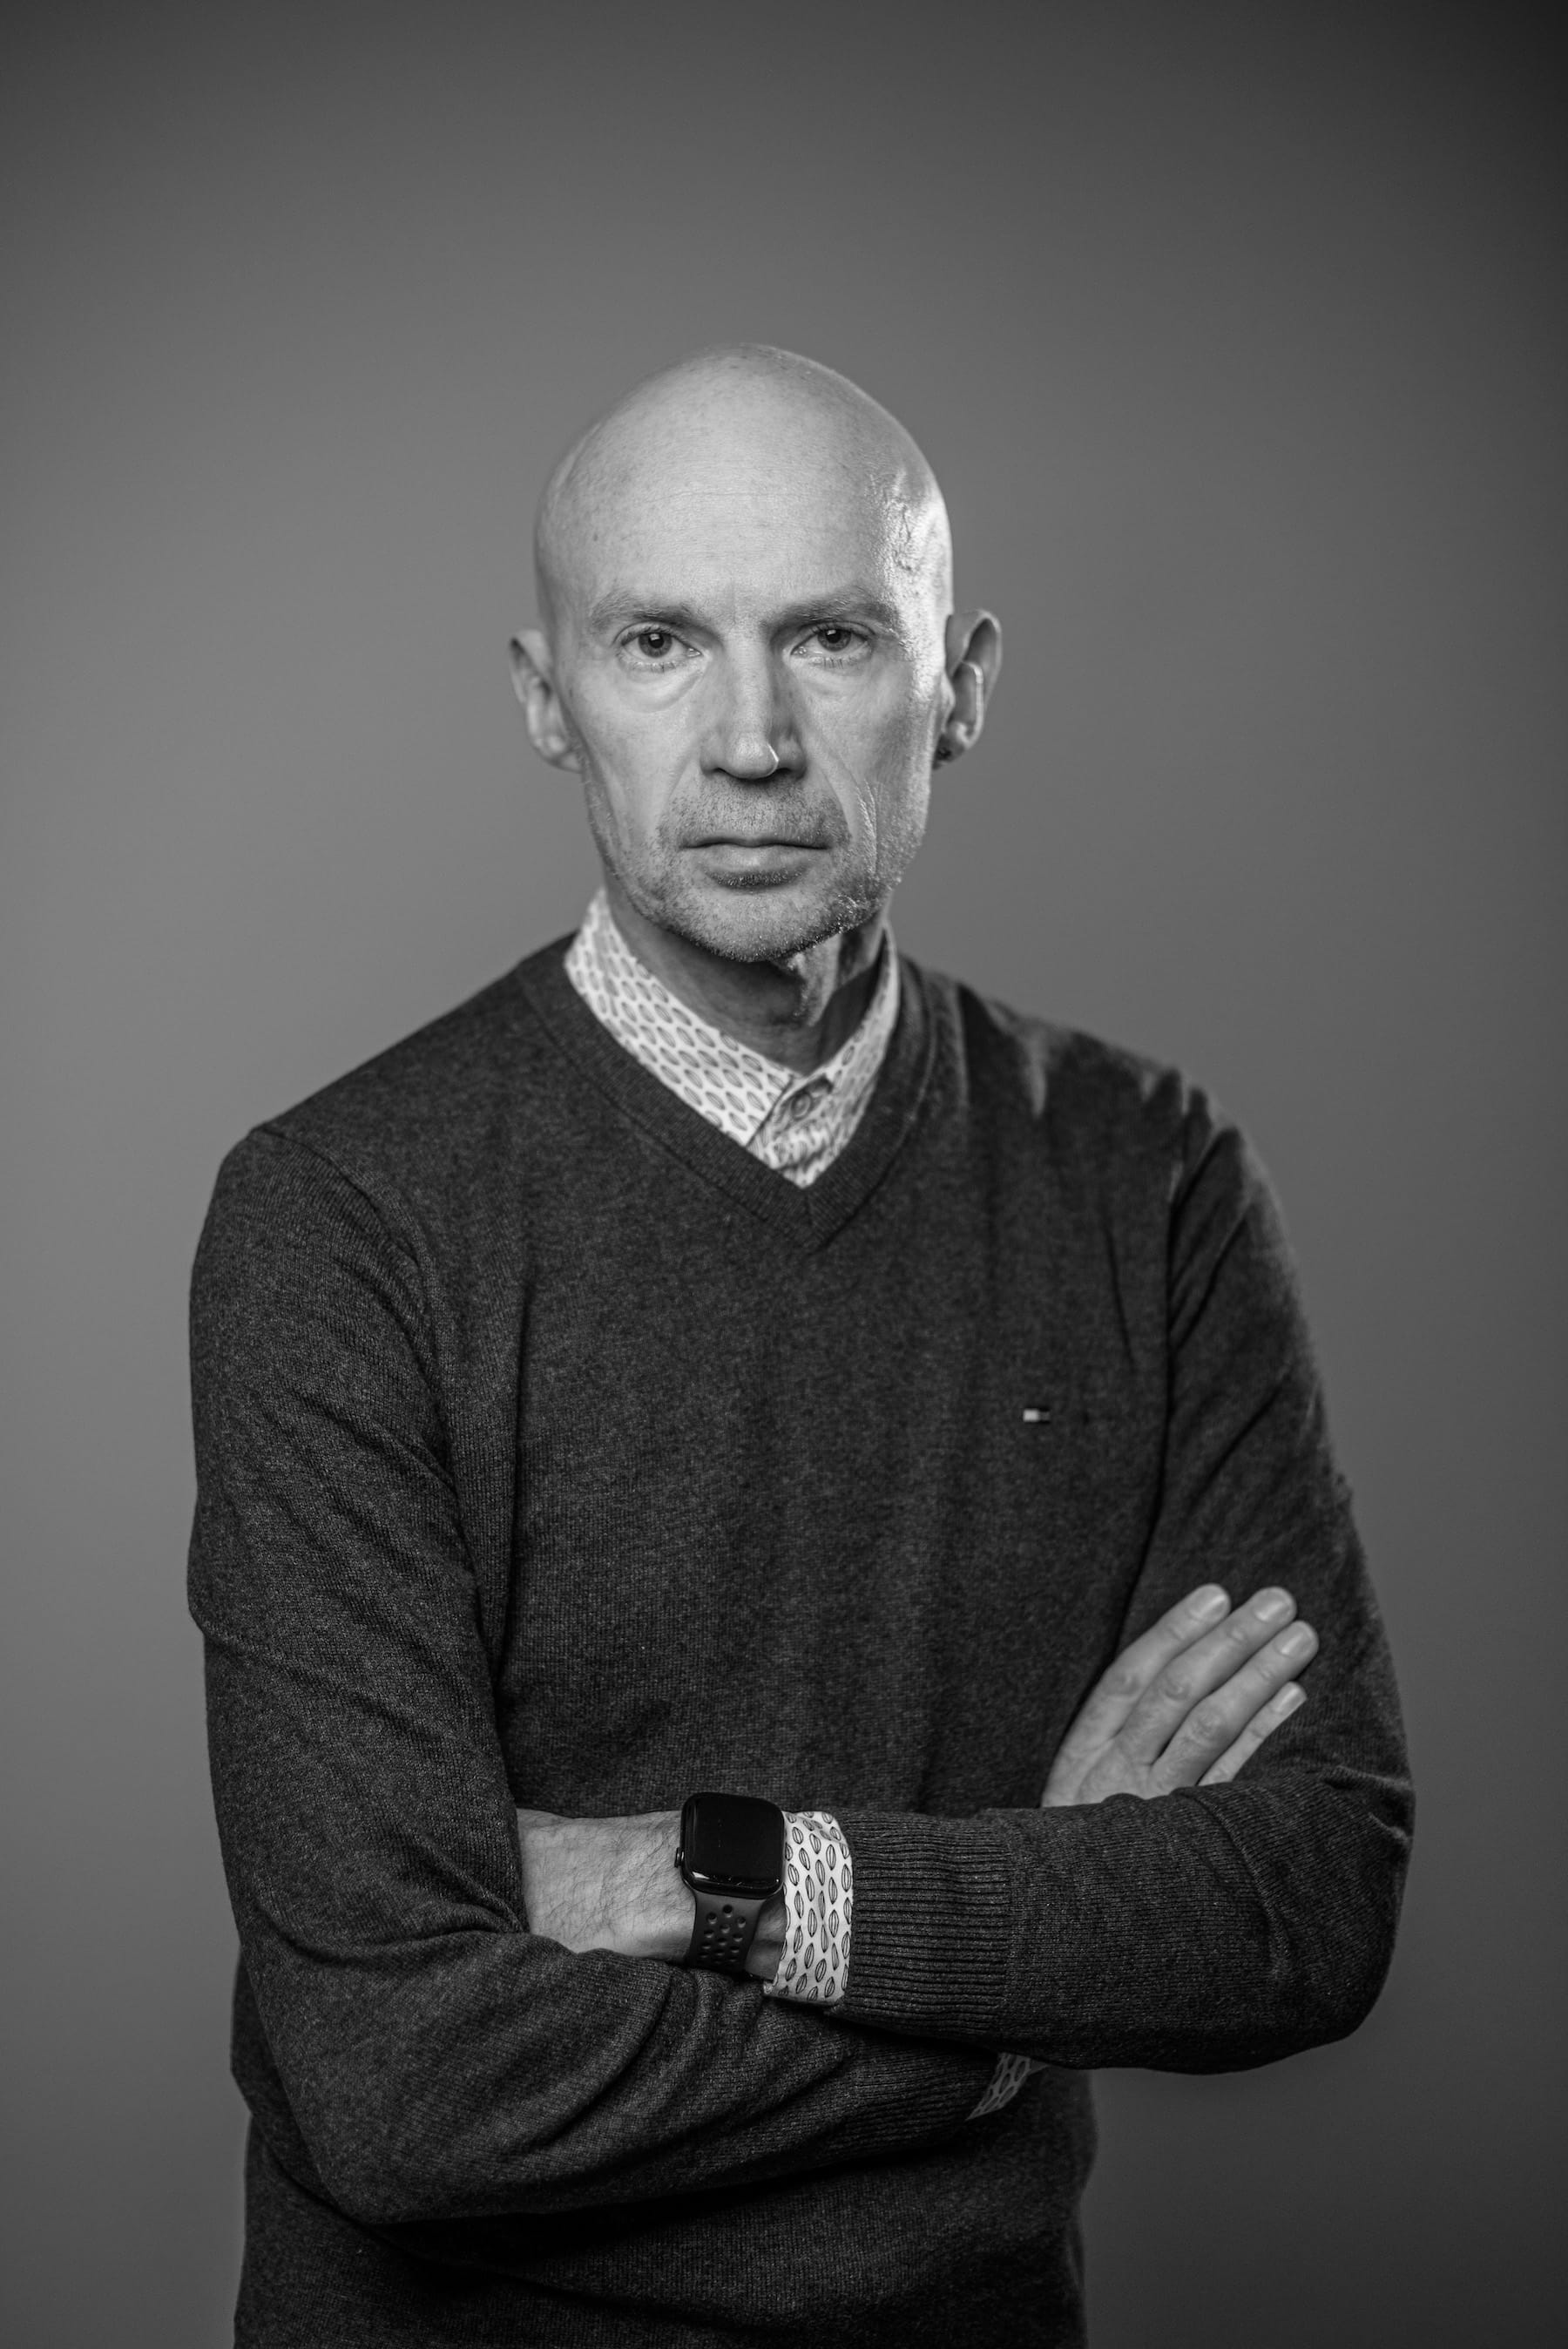
zeroShadow co-founder and CEO Casey Golden explains why this “screening gap” exists, how TIPzs aims to close it and why collaboration across crypto is critical to staying ahead of increasingly sophisticated threats.
What is the screening gap? When an exploit happens, attackers can start moving funds almost immediately, while the intelligence needed to identify those funds as illicit can take much longer to reach investigators, security companies and crypto projects. That delay is the screening gap.
For Casey, co-founder and CEO of zeroShadow, closing it means combining on-chain and off-chain intelligence, reducing false positives and sharing high-confidence threat data in real time.
1inch spoke with Casey about the screening gap, zeroShadow’s TIPzs threat intelligence platform and what the crypto industry needs to do next. zeroShadow is a security partner of 1inch, working with the team on incident response and threat intelligence.
What exactly is the screening gap in crypto today? What kinds of threats are most likely to slip through existing wallet screening and blockchain analytics systems?
I think there are three high-level categories. One is recent exploits - things that happened yesterday or today. There is always a time delay between an exploit happening and knowing it's an exploit. As the different threat actors move the funds, the most sophisticated actors, especially those from nation states like North Korea, have a plan to move the money really fast to try to get through that first wave of obfuscation.
Those things happen in a matter of minutes and even seconds. Producing actionable intelligence to screen against this type of activity only works when you have senior level investigators working around the clock, deploying their intelligence and using their honed skill sets to track these things in real time because there are no existing trails or data to train AI agents on. It's all new. Historical data, no matter how big it is, doesn't really matter for things that happen today.
The second category is laundered funds. You have to use a lot of multidimensional datasets to get through, for example, Tornado Cash, Wasabi or other mixers, or to determine if there has been a change of hands to a money-mule or other entity. That's another area where you need high-quality signals because you don't want to dilute the signal with too much noise. A lot of blockchain analytics companies might provide exposure, but it's just noise. They don't really know exactly who the bad actors are coming out of those mixers and other systems.
Then there's new criminal infrastructure. For example, pig-butchering operations may put up a new website for scams or investment fraud. Victims haven't reported it yet, and this probably isn't something that's discovered by on-chain analytics alone because the primary source exists in Web2 and other domains.
The speed at which they're able to replicate and create new instances of sites, domains and software packages is exceptionally high right now. But even though there are new ways to solicit and get the money in, the pipes out are typically the same. A lot of the time, it's about how fast we can connect the dots to existing infrastructure where illicit money is moving and then work backwards.
Companies that aren't actively working on that threat intelligence every day are going to miss things in their screening capabilities.
Why does the screening gap exist in the first place?
At a high level, the existing systems for screening are like traditional media - newspapers and TV shows. The criminals can only be caught through something more like social media, where you have people on the street, cameras everywhere and what happened 10 seconds ago is already published.
That's the gap. You're not going to catch people with the news at 5 p.m. It's happening the next minute.
The screening gap exists because information sharing has historically been quite slow, and we have to make that as real-time as possible.
How important is speed? At what point does threat intelligence become too late to be useful?
Some bad actors move very fast and furiously. It's basically a flood that moves super fast. Then there are others who are more patient. They're waiting for the right moment to move.
It starts to fall apart when we lose coordination. We have to work with projects like 1inch, exchanges and all the people who provide different products and services throughout the industry.
We have to think about it as a collective network of intelligence and people sharing information. It's like a neighborhood watch program. That's really the only way we can keep up to speed with the bad actors.
A critical element is how quickly you can share intelligence securely. That's really what we've built out and now have available — the rails that let you share information quickly and securely between the different parties that are part of this collaborative network.
We also have to rely on actionable data. Whenever there's an estimate of criminal activity, it's going to slow the process down. It's not a yes-or-no answer. It's a maybe, and that may require human intervention.
Our focus is trying to provide highly actionable intelligence. You have to have a black-and-white signal. Gray is just too fuzzy.
We provide evidence-based modeling. We don't do exposure, which is a theoretical estimate of how much something is bad or good. For us, we know that it's the criminal or not. It's very binary, and that's how you can make decisions quickly.
But you also have to continue adapting. Once we figure out the fingerprint of bad actors and how their pattern flows through a certain way to try to hide their money, and we stop that flow, it's like a stream - it finds another way around.
That forces us to continue to adapt and learn. We need high-fidelity signals for intelligence, but we also need to work collaboratively to adapt and innovate when anything changes.
How does zeroShadow's TIPzs threat intelligence platform work in practice?
We break TIPzs down into three different phases.
The first is setting up the intelligence rails - the communication rails between the source of intelligence and all the people who need to use that intelligence. We make a super-fast connection to make sure that anybody who has important information is able to act on it almost immediately.
The second part is intelligence distribution. On these rails, we distribute the intelligence.
What we've built is that from the time any of our investigators or intelligence providers publishes a new piece of information, it takes less than two seconds to be actionable on the other side. Pretty much by the time I finish this sentence, it's in your screening software, ready to make a block.
That's a huge transformation compared with a year ago, when it might take 12 hours, a day or two days to update all of the infrastructure to house that new information.
For the users of the intelligence, they don't have to change anything. The blocklist files with the new illicit addresses automatically update every few seconds. They just keep screening, doing their standard thing. Their API calls are all the same: is this a good transaction or bad?
We've done all the work under the hood to make that simple and consistent while addressing some of the speed issues we talked about before.
Why is aggregating threat intelligence from multiple sources so important?
There are exceptionally good people who have very precise specialties.
Some people are really good at discovering pig-butchering infrastructure. They're not as good at discovering smart contract exploit vulnerabilities.
We have this beautiful decentralized world where people have amazing areas of expertize and novel intelligence, but they are by nature decentralized. It's our job to take all these different specialties and insights and bring them together so that it's easy for a user, a payment processor or a DeFi protocol. They get the best of all worlds.
The other important aspect is that if we historically looked at just relying on on-chain activity for providing intelligence, it's a very limited scope.
Now we have multidimensional datasets. It's not just your on-chain activity. It's off-chain data and how you're using a system - all these behavioral things that go into composing something unique.
Different companies and different parts of the ecosystem have access to different data dimensions. Combining those helps us create the best picture for the highest quality and success rate in preventing bad actors and catching them if they have already committed the crime.
More screening can also produce more false positives. How does TIPzs distinguish genuine threats from incidental exposure to suspicious funds?
The primary way we make sure there isn't noise is that we only use primary evidence. We don't use the exposure model.
Let's say 10 people deposit $1 million each into a service. Nine of them are upstanding global citizens and one is a criminal who stole funds. They then all take their $1 million out. Under the exposure model, all ten of them would be labeled as having 10% illicit fund exposure. Nine are innocent bystanders, but they all get tarnished the same. For the good people, this creates serious problems and false positives, but for the bad actors, this is great. We see them continuing to use this strategy to rinse and repeat this, and thereby tainting many other innocent folks with incorrect ‘exposure’, while driving down their own rating low enough to then fly under the compliance radar.
What we do is make sure it's not about exposure. It's about the bad actor in and the bad actor out. It's one-to-one. We make sure the nine who are not bad are cleared, and the only bad one is identified based on evidence.
Every decision is backed by a full set of provable data that could go to court. That's how we get rid of a huge amount of noise. It's a lot harder to do because you have to have a human in the process or more complex computational models that use different dimensions.
There have been situations where screening tools stopped a huge number of people from using a service not because they did anything bad, but because a bad actor dusted their wallets with some illicit funds - $2, $3 or $5. They didn't do anything wrong. It's a bad actor playing games and trying to create a distraction.
Through evidence, we know who the bad actor is. Those who received funds through this mechanism are not bad. That's just one example of how an evidence-based approach versus exposure helps us reduce the noise as much as possible.
For a DeFi project like 1inch, how can real-time threat intelligence improve security without undermining DeFi's permissionless and non-custodial principles?
The first way we can make sure that people who use DeFi and 1inch can retain the permissionless principles is is to get rid of false positives.
We've had so many cases where fully legitimate DeFi users are stopped from using a service. They're not given that freedom anymore because it's a false positive.
Making sure false positives are minimized as much as possible is critically important.
The second way is real-time intelligence. The better we can share real-time intelligence, the better we can keep the poison out of the water. If bad actors are kept away from an ecosystem, then the exposure of people using that project is significantly less.
It's our job to make sure their funds, wallets and usage are kept as clean as possible by having better security and better screening.
A lot of the work that 1inch is doing is leading the industry in a variety of ways. 1inch is setting a really high-quality standard.
What needs to change to make the screening gap smaller?
All of it - technology, intelligence sharing and cooperation.
Sometimes it's heavy on technology and light on intelligence sharing. Other times it's heavy on cooperation and intelligence sharing, while the technology is already in place. Over time, which piece of this recipe is really required will continue to evolve.
We have to continue advancing the technology at the rate and speed at which bad actors are working. That's always going to be a challenge: making sure we can detect, share and move as quickly as they do.
Intelligence sharing will become even more critical. If we can continue to create a much more robust and comprehensive network of sharing, that's how we understand how to keep each other safe. If you see something bad, tell somebody you saw something bad. That will keep the whole ecosystem much healthier overall.
Continual innovation is also important. Whether it's AI tools, different techniques or privacy protocols, there's always going to be strong innovation in this space. We have to make sure we're using these new tools and technology to the best of our ability because the bad guys surely will.
We need to innovate together in a collaborative way.
The other side is regulatory support. By that, I mean more guidance from a global perspective - not restrictions, but recognition for those who are part of this network, sharing information and helping keep things safe.
If governments can support businesses in the DeFi space that are meeting certain standards for security and protection of their users, I think there are things that can be done to incentivize and collaborate.
At the end of the day, we're trying to keep people safe. A lot of people work really hard for their money, and we want it to stay in their hands and not go to the criminals.
Is there anything else the industry needs to do?
We're starting to get a lot more coordination between the public and private sectors in terms of intelligence.
When we're working with different law enforcement agencies around the world, the question is: how are we helping them pursue their cases and how are we getting information about the victims they are serving out to the industry and then actioned?
Closing the gap also means forging a stronger relationship between the public and private sectors, sharing intelligence and coordinating on frameworks so everybody is speaking the same language. Over the next year or so, I think we're going to see some really nice advancements in frameworks. The cyber world has had things like the cyber kill chain. I think we're going to start seeing some development around how things can be reconstructed in parallel in the crypto world.
That will help public and private organizations work together. It can also provide better understanding and insight from an enforcement and judicial perspective.
Those things will be very helpful as we think about how to make the industry safer while keeping its freedoms and benefits available at the same time.
For more on security, subscribe to our newsletter.
zeroShadow is a security partner of 1inch. The views expressed in this interview are those of the interviewee and do not necessarily reflect the views of 1inch. Product descriptions are the interviewee’s own. This content is for general information purposes only and does not constitute legal, compliance or investment advice.
Join us


